CloudTrail Investigation
Took the EC2 instance from Lab 1 and reconstructed its full API activity history from CloudTrail. The skill of separating routine background noise from the one or two events that actually matter, and proving a negative as rigorously as a positive.
Method
Filtered CloudTrail Event history by Resource name = i-051c67c4e41f6b391, no date restriction. Event history covers the last 90 days by default. This returned 26 events total.
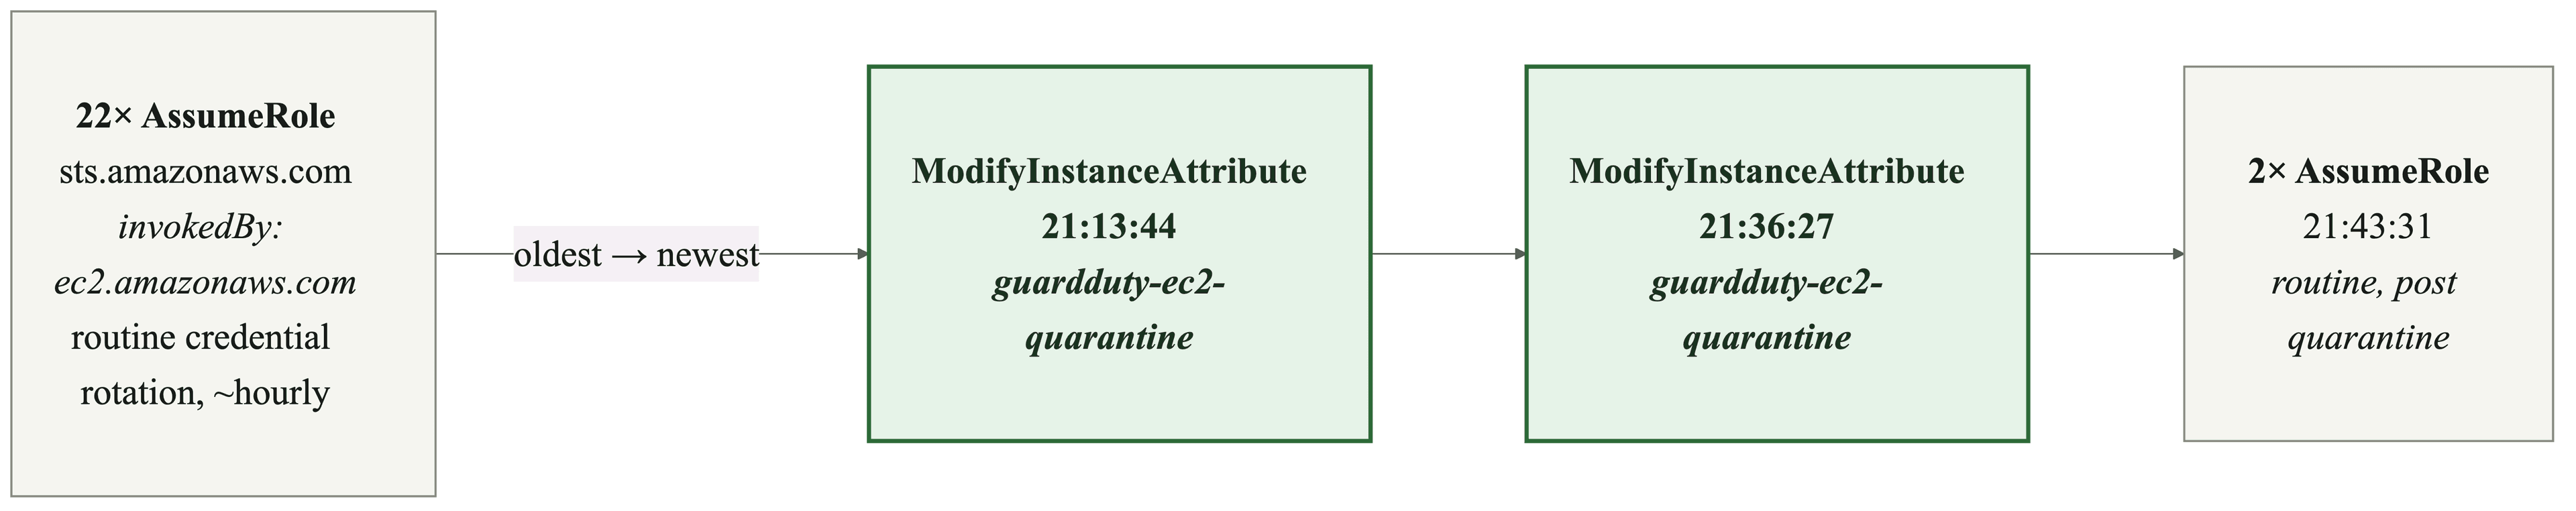
Baseline: what the AssumeRole noise actually is
24 of the 26 events are AssumeRole calls via sts.amazonaws.com, recurring roughly hourly. I opened one to confirm what was generating it rather than assume:
"userIdentity": {
  "type": "AWSService",
  "invokedBy": "ec2.amazonaws.com"
}
Source IP was the service principal ec2.amazonaws.com, not a real network address. This is EC2 itself automatically refreshing the instance’s IAM role derived temporary credentials, which every instance with an attached role does roughly hourly via the instance metadata service. Not a person, not an external caller, scoped to nothing beyond what guardduty_ec2_role already allows. Expected, benign, ruled out as noise.
The two events that actually matter
The two ModifyInstanceAttribute calls are the only events on this instance’s entire 90 day history where its configuration actually changed. Both came from the guardduty-ec2-quarantine Lambda’s execution session, targeted exactly this instance and the known quarantine security group, and line up in time with the two controlled test invocations from Lab 1. The second run confirming the operation is idempotent when reapplied to an already quarantined instance.
Every one of the 26 events is accounted for. 24 are routine EC2 service credential rotation; 2 are the known, intentional quarantine actions, both attributable, both expected, at the exact timestamps expected. The absence of any other event type (no unexpected instance launches, no security group rule changes from an unrecognized principal, no console logins against this instance) is itself part of the finding.
Evidence
Full detail for one of the two ModifyInstanceAttribute calls is captured in Lab 1’s evidence. It doubles as this lab’s anomalous event detail.
I filtered CloudTrail's Event history down to just this instance's resource name and pulled the full 90 day window. 26 events came back, and my first move was to group them by event name before drawing any conclusions from the raw list.
The AssumeRole calls made up most of the 26 events, so before dismissing them as noise I opened one to actually confirm what was generating it. userIdentity showed AWSService, invokedBy ec2.amazonaws.com, which told me this was routine credential rotation, not a person or an outside caller.